
Bring the method into your organisation.
Cyber regulatory compliance services, artificial intelligence use case assessment, governance build, retained advisory and executive education, all run on the DICB method. Every engagement is scoped before it is priced.
Governance
Who owns the decision, under what authority, and what the record shows.
Regulation
What the law requires today, what is draft, what is proposed, and the difference.
Evidence
What an organisation can actually demonstrate, to a board, an auditor or a regulator.
Five ways to work with DICB
Each one answers a question your organisation is already being asked. Each one produces a record another professional can test, not a report that sits in a drawer.
Cyber regulatory compliance services
Our core service. We take a regulation that applies to you and translate it, using the DICB Cyber Regulatory Translation Standard, into obligations your organisation can run: one record per duty, with its scope, controls, accountable owner, state and the evidence each claim needs. Readiness assessments before a regulator or auditor arrives. Evidence reviews that tell you what will hold and what will not.
Artificial intelligence use case assessment
One use case, assessed from every angle that will be asked about it: legal, technology, cyber, data protection, policy and compliance. We screen it against the law as it stands today and label what is draft or proposed as draft or proposed. We identify the controls, the owner, the evidence that should exist, and the decision leadership has to make.
Governance build
Policies, registers, ownership and review triggers designed so that the compliance state lives in the institution, not in one person. Built to be maintained: which events reopen a record, who reviews what, and how the board sees it.
Retained advisory
The questions that arrive between projects: a new guideline, a supplier incident, a request from a regulator, a use case nobody saw coming. A retained arrangement gives your team a practitioner to put them to, with a written answer that goes on the record.
Executive education, in house
In-house executive briefings on named topics, private cohorts on the DICB-CCRP course, and bespoke workshops built around your own regulation and your own systems. Self-paced versions of some briefings are published as online modules for teams that prefer to work at their own pace.
Named topics, not a generic awareness session
Each briefing is half a day or less, in your boardroom or online, built so that the people in the room leave with a decision format they can use the following week.
Artificial intelligence risk and governance: from policy to evidence
The Nairobi workshop, delivered privately. One real use case carried from assessment to a decision.
What the board should ask before signing
The five questions, the one-page briefing format, and what a defensible answer looks like.
Kenya’s Data Protection Act 2019 for decision-makers
What binds today: principles, rights, registration, impact assessments, automated decisions, enforcement to date.
Evidence quality: what an auditor will accept
Design evidence against operating evidence, the TRACE test, and why a policy does not prove a control worked.
Third-party and supplier risk you can prove
What the supplier actually retains, what the contract says, and what evidence you hold on the day it matters.
Draft and proposed regulation: how to prepare without over-reacting
Reading supervisory direction and draft guidelines for what they signal, without recording a strategy as a law.
Scoped first, priced second
We do not publish price lists because no two estates are the same, and a price given before scoping is a guess dressed as a quote. Every engagement follows the same four steps.
A conversation
Thirty minutes on what you are being asked, by whom, and what you would like to be able to prove. No charge.
A written scope
What we will do, what you will have at the end, who needs to be involved on your side, and the price for exactly that.
Delivery on the method
Every engagement uses the same standards described on the Method page, so the output is testable by anyone who knows them.
Handover, not dependency
Your people own the record and know how to keep it current. We leave; the governance stays.

DICB does not certify governance it built
Independence is part of the method. If DICB builds your governance, it will not later assess it for certification; if DICB assesses, it did not build. Legal review is carried out through our advocate partners, so a regulatory interpretation is checked by a practising lawyer before it reaches your record.
DICB operates from Nairobi and the Isle of Man and works remotely with organisations elsewhere. Engagements are contracted through DICB’s operating entity in the relevant jurisdiction.
Nairobi, 31 October 2026
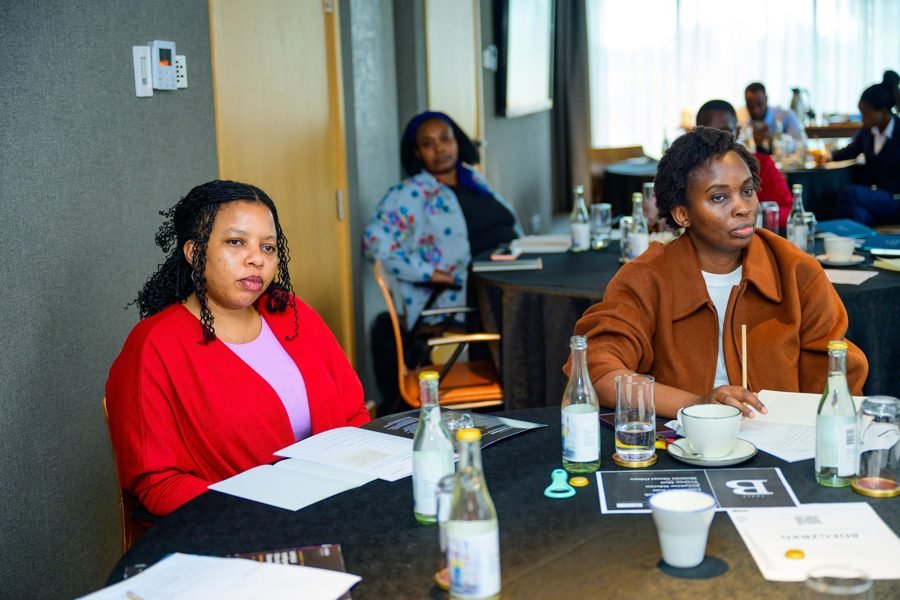
DICB’s first executive workshop in Kenya sold out. Thirty professionals from banking, law, technology, insurance and government assessed a real artificial intelligence use case, built a risk register entry, screened it against Kenyan law and wrote a one-page briefing their leadership could act on. The same morning can run in your boardroom.

Tell us what you need
Two minutes. We come back within two working days to arrange the first conversation.
If you would rather write, email contact@drikhalia-cyberbootcamp.com with the regulation, the use case or the decision in front of you.
Your details are used only to respond to this enquiry. Privacy policy.
A control is not what the policy says should happen. It is what you can prove happened.Dr Joseph Ikhalia