Knowing what a regulation says. Proving how you comply.
Dr Ikhalia Cyber Bootcamp is a specialist cyber regulatory education and capability-development platform built around three disciplines: Governance, Regulation and Evidence.
Governance
Who owns the decision, under what authority, and what the record shows.
Regulation
What the law requires today, what is draft, what is proposed, and the difference.
Evidence
What an organisation can actually demonstrate, to a board, an auditor or a regulator.
Not a beginner cybersecurity bootcamp
DICB’s purpose is to develop professionals who can interpret regulatory requirements, translate them into accountable operational obligations, determine what evidence should exist and make defensible assurance judgements about whether those obligations are actually being met.
The intellectual foundation of DICB is Dr Joseph Ikhalia’s published paper, The Three Problems of Cyber Regulatory Compliance: Translation, Institutional Continuity, and Evidence Quality. That research underpins the DICB Cyber Compliance Model™ and a growing controlled intellectual-property system for evidence-led regulatory compliance.
The DICB methodology includes the Cyber Regulatory Translation Standard™, Canonical Obligation Record, Obligarium™ Cyber Compliance Digital Twin, TRACE Evidence Standard™, Evidence Matrix, Evidence Decay Model, Cyber Compliance Method, DICB-CCRP professional designation and Compliance Benchmark. Together, these components provide a repeatable method for converting regulation into governed obligations, controls, evidence and assurance conclusions.
Its flagship course, the DICB Certified Cyber Regulatory Practitioner (DICB-CCRP), takes that methodology into professional practice, developing the judgement required to work across regulation, governance, evidence, accountability and senior-level decision-making.
DICB exists to close the gap between knowing what regulation says and being able to demonstrate, with evidence, how an organisation complies.

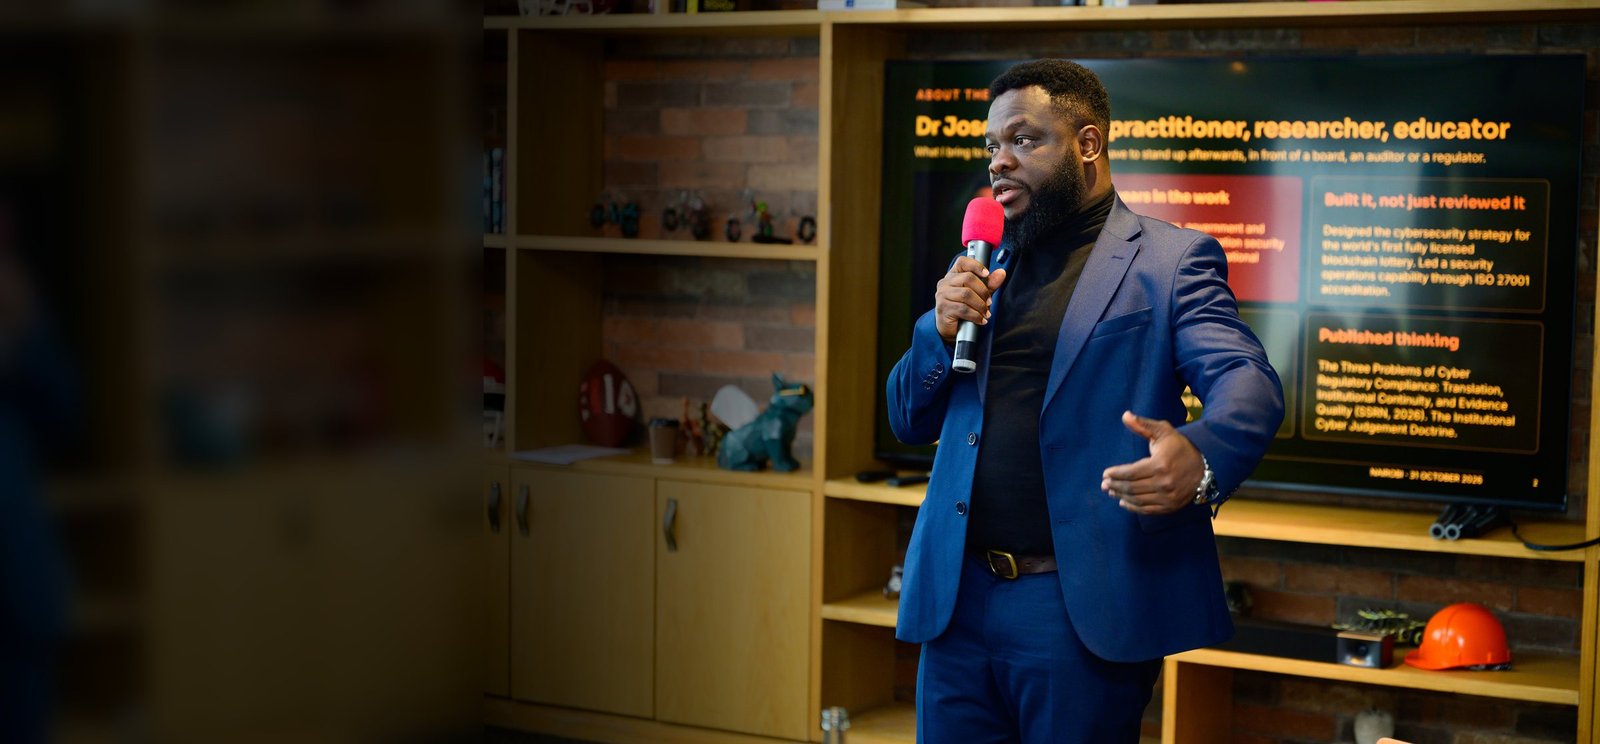
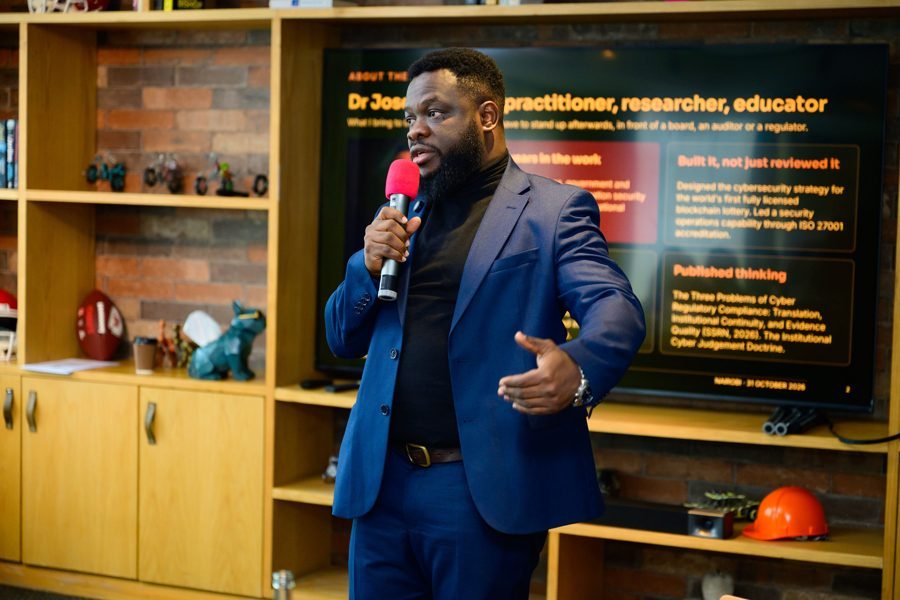
Dr Joseph Ikhalia
Information security governance leader, researcher and practitioner.
Dr Joseph Ikhalia is an information security governance leader, researcher and practitioner with more than 15 years’ experience across financial services, government and technology. He holds a PhD in Computer Science from Brunel University London, where his doctoral research produced Social Network Criminal, an early security-awareness application built within a social network. The work received Brunel’s Dean’s Award for Innovation and Impact, won a Best Paper award at an international conference in Mannheim and was subsequently published in Information Technology & People.
His career has ranged from designing the cybersecurity strategy for the world’s first fully licensed blockchain lottery and leading a security operations capability through ISO 27001 accreditation, to information security governance within an international financial services group. His current work spans cyber governance, regulatory alignment, artificial intelligence governance, assurance, third-party risk and board-level evidence.
Dr Ikhalia is also the author of The Three Problems of Cyber Regulatory Compliance: Translation, Institutional Continuity, and Evidence Quality, published on SSRN in 2026, and the Institutional Cyber Judgement Doctrine. His wider work examines how organisations make, evidence and defend consequential cyber decisions.
He has contributed to Brunel University’s Industry Advisory Board and spoken at CyberIsle, the London Law Expo and other professional forums. Across his research, professional practice and teaching, one theme is consistent: moving cyber governance beyond policy and compliance language towards evidence, judgement and decisions that can withstand scrutiny.
Published, and open to challenge
The problem analysis behind DICB is published so that it can be tested separately from the DICB codification that answers it. The Three Problems of Cyber Regulatory Compliance (SSRN, July 2026) sets out three structural deficits, derives seven requirements for an adequate discipline, and proposes the DICB Cyber Compliance Model as one candidate codification. Its limitations are stated in the paper itself.
The Institutional Cyber Judgement Doctrine sits alongside it: how organisations make, evidence and defend consequential cyber decisions.
Nairobi and the Isle of Man
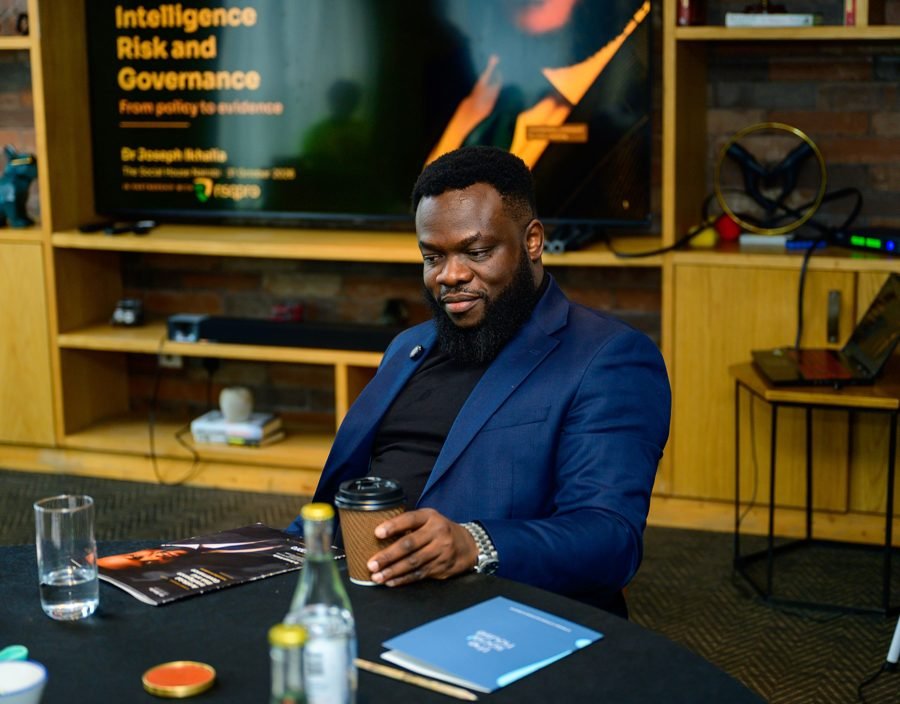
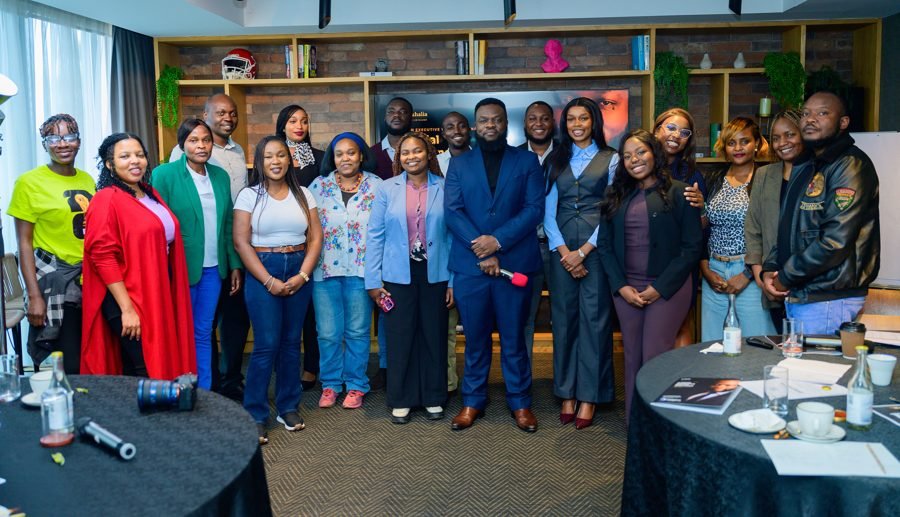
DICB operates from Nairobi, Kenya and the Isle of Man. In Kenya it is building a bench of practitioners, working with firms and professional communities, and running executive education for the people who approve, assess and defend the use of technology. Its first executive workshop, Artificial Intelligence Risk and Governance: From Policy to Evidence, sold out in Nairobi on 31 October 2026, in partnership with RisqPro Group.
DICB Kenya is supported by a team across legal community, business development and engagement, with advocate partners for legal review.
Governance. Regulation. Evidence.The three disciplines of Dr Ikhalia Cyber Bootcamp