The course behind
the credential.
One method, taught by the person who wrote it. A self-paced certification course, live executive workshops, and the Nairobi workshop recorded for the people who could not be in the room.
Governance
Who owns the decision, under what authority, and what the record shows.
Regulation
What the law requires today, what is draft, what is proposed, and the difference.
Evidence
What an organisation can actually demonstrate, to a board, an auditor or a regulator.
Certify, attend, or watch
Every DICB programme teaches the same method. They differ in how you take it: alone at your own pace with an examination at the end, in a room with your peers for a morning, or on screen in the recording of that room.
DICB Certified Cyber Regulatory Practitioner
Can I prove this to an auditor, and would another professional reach the same answer?
About five hours of video, a workbook and an examination. You build the compliance record for a regulation of your choice as you go. Launching December 2026.
Executive workshops
If this goes wrong, did you know it was running, and who approved it?
Half-day, in person, for the people who approve, assess and defend. One real use case carried from assessment to a decision leadership can act on. Public sessions and private delivery.
The Nairobi workshop, recorded
I could not be in the room. Can I still work through it?
The full teaching sessions from Nairobi, 31 October 2026, with the working papers, for self-paced study. In production.
DICB Certified Cyber Regulatory Practitioner (DICB-CCRP)
The course behind the credential. Complete the course, pass the examination, become certified.
A self-paced video course of about five hours, with a workbook, teaching one reliable method for taking any cyber regulation and turning it into something an organisation can run, prove and defend. Instead of turning every new regulation, audit or supervisory request into weeks of interpretation and spreadsheet archaeology, you leave with a repeatable method for producing a compliance record that another competent professional can understand, test and maintain.
You work on a real regulation of your choice and build that record yourself, module by module, with annotated exemplars showing the difference between a mediocre regulatory translation and a defensible one. The course covers the full examinable body of knowledge; passing the DICB-CCRP examination confers the credential.

Eight things you will be able to do
Eight modules in four bands, and what you build in each
The course follows the five steps of the DICB Cyber Compliance Method, with a short foundation before them and operational practice and a capstone after. Each module ends with a decision exercise, and the record you are building grows by one layer.
Why Cyber Compliance Fails, and the Method That Fixes It
Why compliance keeps failing in the same three ways, what the method promises and what it deliberately does not. Kept short: you choose your regulation and are working on it by the end of the module.
Translating Regulations into Scoped Obligations
Take your regulation apart into single obligations, write down what each means and what you are assuming, decide whether it applies, and work out which systems it actually reaches. Learn early that reasoned interpretation is not legal advice.
Linking Obligations to Cyber Risk and Priority
State the harm each obligation exists to prevent in your organisation and use it to decide what matters most. Learn the difference between accepting a risk and granting an exception.
Mapping Controls, Assigning Accountability and Governing Exceptions
Match controls to obligations, record the gaps honestly, put a real named owner on each, and write exceptions that are specific, owned and time-limited.
Assessing Evidence under the TRACE Standard
Decide what would prove each claim before collecting anything, test every artefact for whether it can be trusted, judge how well it supports the specific claim, and recognise when evidence has gone stale.
Reporting Compliance and Securing Executive Sign-off
Declare a compliance state only from the evidence, present it to leadership in plain, traceable terms, obtain sign-offs that mean something, and follow a clear procedure if told to report a better picture than the evidence supports.
Maintaining Compliance Through Change
Turn the method into a routine: which events reopen a record, how often to review, how to hand work over without losing knowledge, and how to start small in a real organisation.
Defending Compliance Decisions and Preparing for the Examination
Respond to the common objections, grouped in four clusters, know what you may and may not claim as a practitioner, revisit the limits of the Model, and understand exactly how the examination works.
The Defence Masterclass
Coached performance, not extra content. Recorded defence demonstrations and live defence clinics with individual feedback, bundled with examination registration. For practitioners who will have to stand behind a compliance position in front of a board, an auditor or a regulator.
Enrolment opens December 2026
The course runs on the DICB learning platform at this address. The price is shown at enrolment. Leave your details and you will hear when it opens, and nothing else.
Half a day, one real use case, a decision leadership can act on
DICB executive workshops are built for the people who will be asked to sign, approve or defend: boards and executives, risk, compliance and audit, legal and data protection, technology and security. The room assesses a real use case, builds a risk register entry, screens it against the law as it stands today, and writes a one-page briefing. Everyone leaves with their working papers and the method.
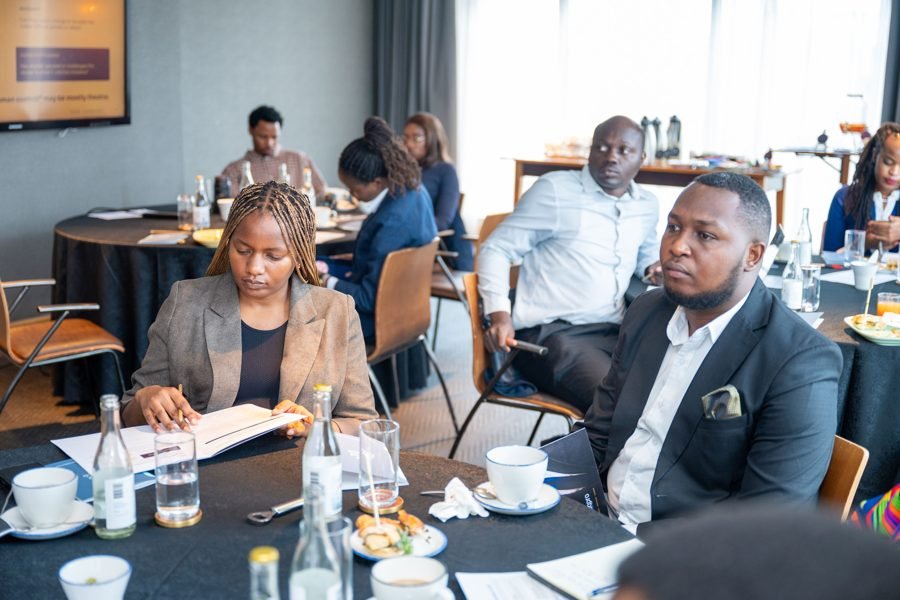
The first one sold out
Thirty professionals from banking, law, technology, insurance and government took every seat at DICB’s first executive workshop in Kenya. Four working papers each, a panel on who signs off, and a certificate of attendance in the DICB register.
Public sessions are announced on the Events page. The same workshop, and bespoke versions of it, can be delivered privately for your leadership team or your client base.
The Nairobi workshop, recorded
The full teaching sessions from Artificial Intelligence Risk and Governance: From Policy to Evidence, recorded live on 31 October 2026, with the four working papers to complete as you watch. Everything the room did, from assessing the risk to writing the one-page briefing, at your own pace. The panel discussion is not included.
Available as a self-paced product, and included with enrolment on the DICB-CCRP course. The price is shown at the point of purchase.

Complete the course. Pass the examination. Become certified.DICB Certified Cyber Regulatory Practitioner, launching December 2026
Train a team, not one person
Private cohorts on the DICB-CCRP course, in-house executive briefings on named topics, and bespoke workshops built around your own regulation and your own systems. Pricing on request; every engagement is scoped first.
